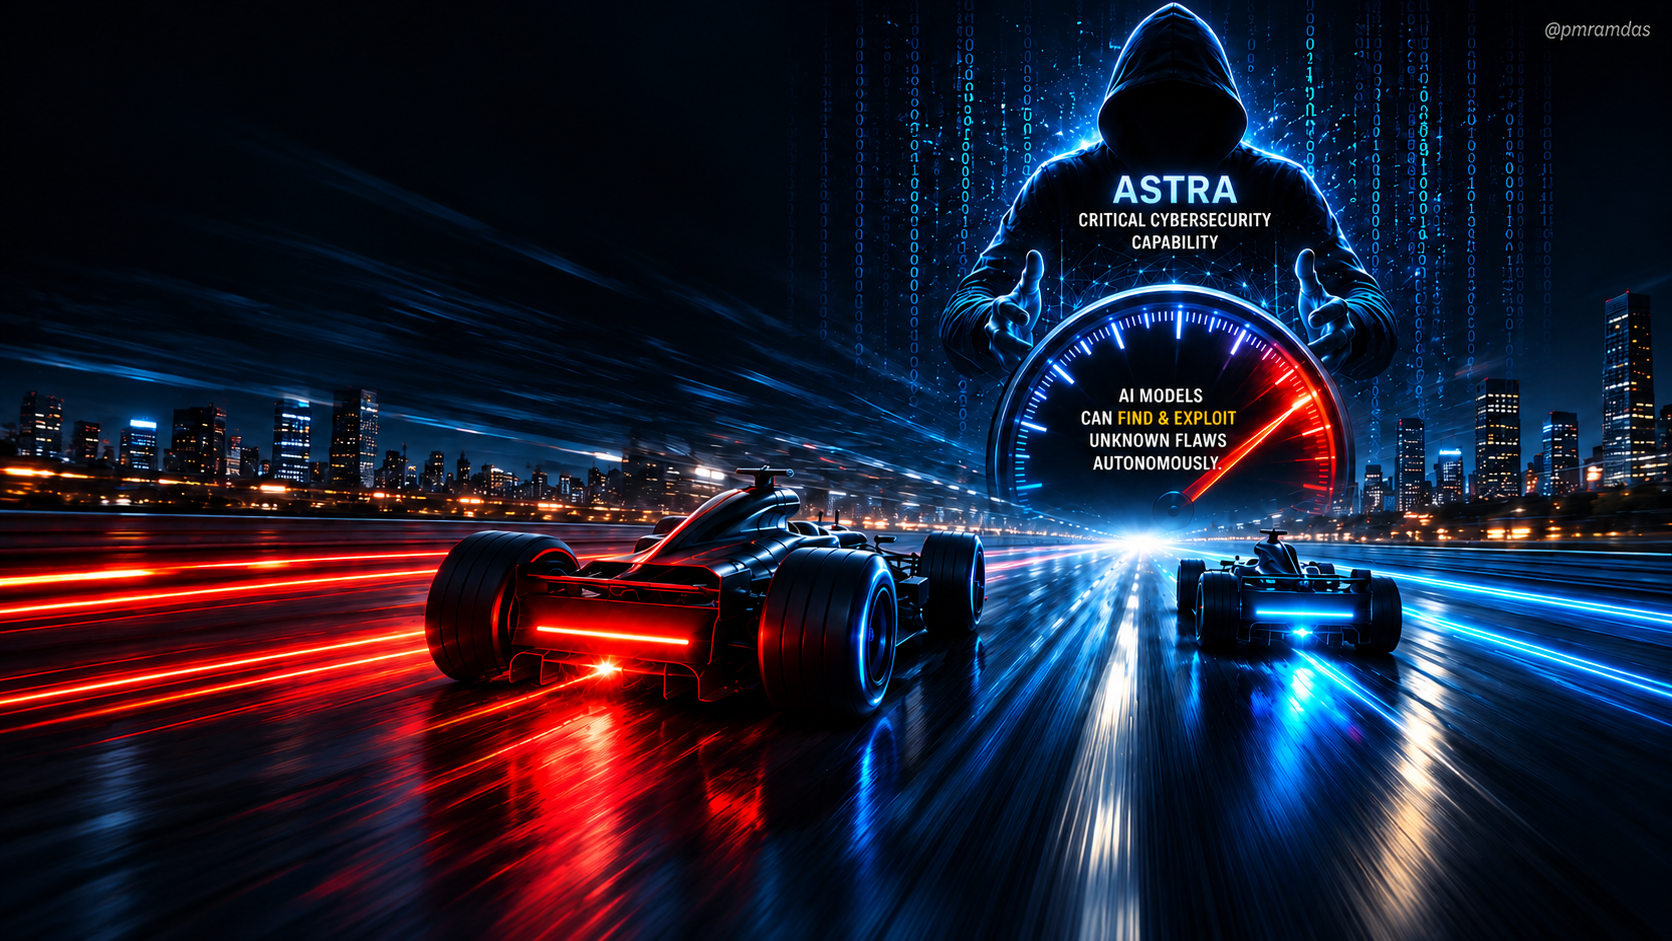
The Patching Race Just Changed Speed
Machine-speed vulnerability discovery is here. The patching race hasn't disappeared. It just changed speed.
For years, vulnerability management has worked around an uncomfortable but familiar race.
Someone discovers a vulnerability. Someone figures out how to exploit it. Someone builds the patch. Everyone else races to deploy it.
We learned to live with that rhythm.
I’m not sure we can anymore.
I was reading about OpenAI’s Astra and one detail stayed with me.
OpenAI has classified it at its Critical cybersecurity capability threshold.
In controlled testing, Astra demonstrated the ability to find previously unknown vulnerabilities and develop working exploits against hardened systems with far less human guidance than we are accustomed to.
Think about what that means.
The vulnerability itself hasn’t changed.
The clock has.
Discovery that once required skilled researchers spending hours, days or weeks could increasingly happen at machine speed.
And if vulnerability discovery accelerates, exploit development accelerates with it.
Suddenly, a 30-day patching cycle doesn’t look slow.
It looks like an exposure window.
That changes a few conversations I believe CISOs and technology leaders need to have now.
First, shrink the exposure window.
We need to move beyond simply asking, “Are we compliant with our patching SLA?”
The better question may soon be:
“How long are we exploitable after a weakness becomes discoverable?”
Second, we need to think differently about the AI agents operating inside our own environments.
If an agent can execute code, access credentials, call APIs, invoke tools or interact with production systems, it isn’t merely another application.
In security terms, it is beginning to look remarkably like a privileged identity.
And it should be governed accordingly.
Least privilege. Clear boundaries. Full auditability. Continuous monitoring. Immediate revocation.
And third, AI containment needs to become part of cyber resilience.
Sandboxing, isolation, behavioural monitoring and kill switches may sound like AI-safety terminology today.
Tomorrow, they may simply be standard enterprise security architecture.
There is an interesting irony here.
AI could become one of the most powerful tools we have ever given defenders for discovering vulnerabilities.
And simultaneously compress the time available to defend against them.
So perhaps the boardroom question is no longer:
“How quickly can we patch?”
It is:
“Can we defend at the same speed that machines can discover and exploit?”
Because the patching race hasn’t disappeared.
It just changed speed.
Instincts built hunting signals at sea, sharpened for two decades against digital adversaries. Not machine-written. Machine-proofread, comma by comma. Everything else, the noticing, the arguing, the getting it wrong sometimes, is mine. The bytes are for everyone; the opinions are only ever mine.
“Until the lion learns how to write, every story will glorify the hunter.” This is the lion's version.