Cybersecurity in Modern Conflict: A Strategic Framework for Organisational Resilience
A cyber defence doctrine tailored for modern asymmetric conflict, from war room protocols to critical infrastructure hardening.
The digital battlefield has become as critical as the physical domain in contemporary conflicts. As cyber threats grow in sophistication and scale, organisations must adopt a militarised approach to cybersecurity, implementing rigorous defences, maintaining constant vigilance, and preparing for multi-vector attacks.
Below is a strategic and technically fortified cybersecurity blueprint, crafted to elevate your organisation’s digital resilience in the face of rapidly advancing threat vectors. This framework draws from globally recognised security standards and empirical incident response protocols.
In an era defined by geopolitical tensions, transnational competition, and escalating conflicts of interest between nation-states and enterprises, the digital domain has become a prime theatre for sophisticated cyber offensives, including those orchestrated by state-sponsored adversaries. As the threat landscape evolves with unprecedented velocity, organisations must prepare for persistent, multi-vector cyberattacks that aim to destabilise, disrupt, and compromise mission-critical infrastructure. This blueprint serves not just as a guide, but as a cyber defence doctrine tailored for modern asymmetric conflict.
Rapid mobilisation: incident response and continuous monitoring
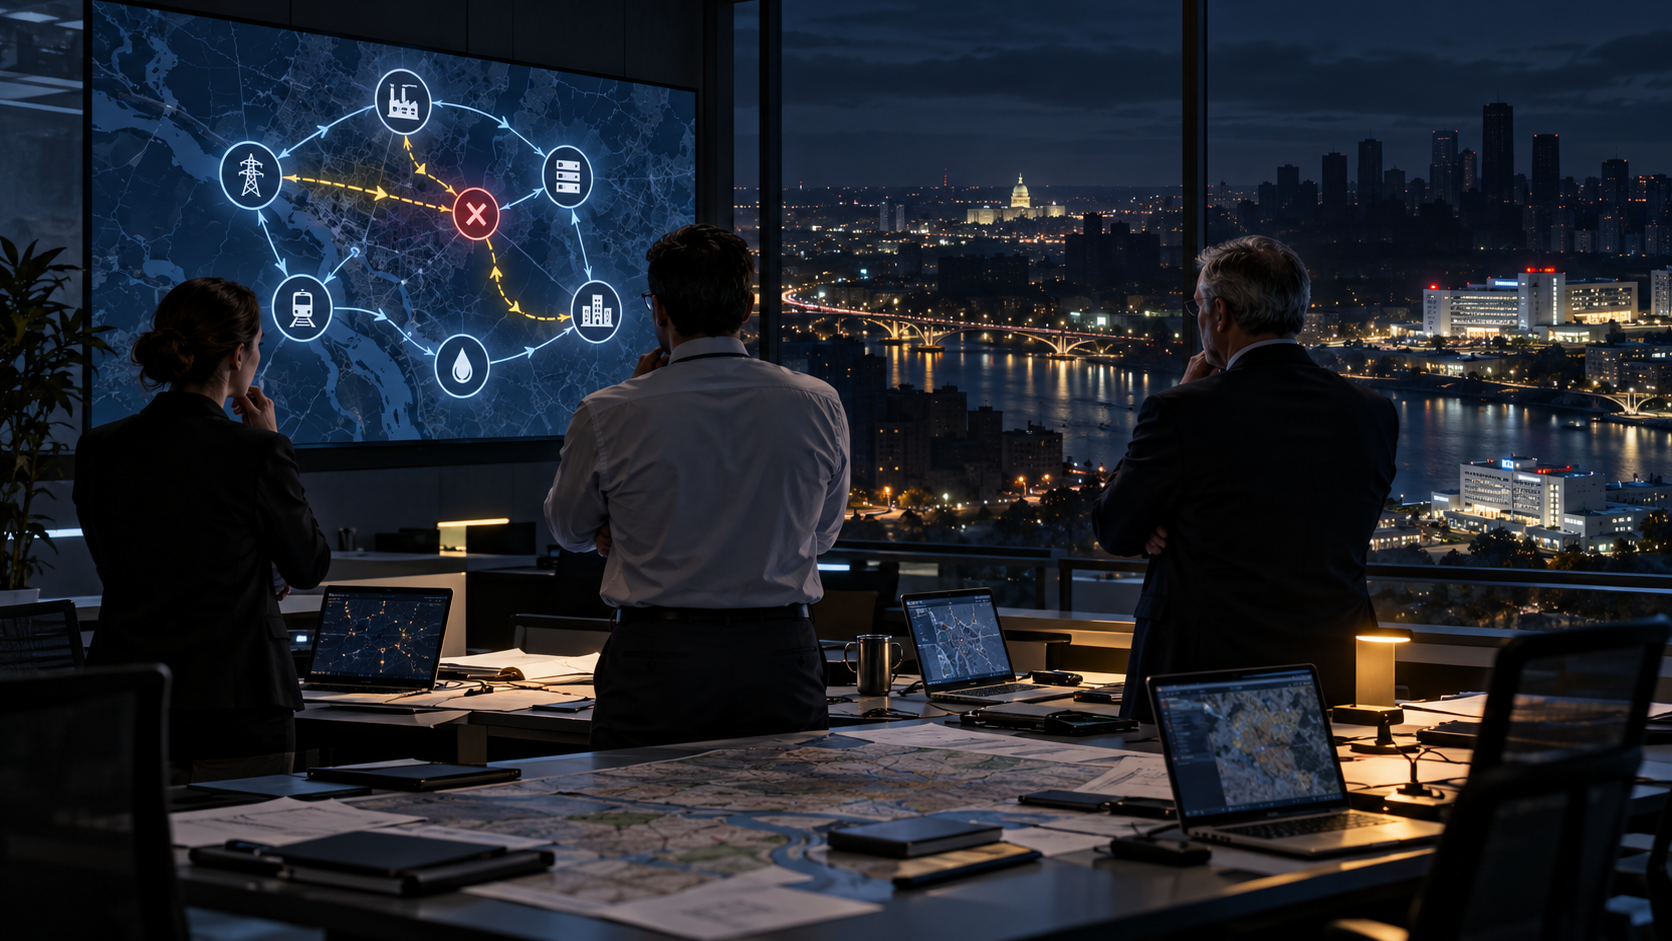
Establishing a cybersecurity war room. A dedicated 24/7 war room serves as the nerve centre for threat detection and response. This operational hub integrates cross-functional teams (IT, legal, communications, and executive leadership), enabling real-time decision-making. As observed in federal playbooks, war rooms streamline coordination during crises by centralising tools like SIEM systems, threat intelligence feeds, and incident tracking dashboards. For distributed teams, virtual war rooms leverage encrypted collaboration platforms to ensure secure communication while maintaining situational awareness.
Asset audits and network hardening. Immediately isolate previously compromised systems and conduct full-scope vulnerability scans using tools like Nessus or Qualys to identify unpatched CVEs. Prioritise assets handling sensitive data (Active Directory servers, database clusters) for offline remediation. Red teams should simulate adversarial tactics, such as lateral movement via EternalBlue exploits, to stress-test network segmentation.
Incident response plan validation. Update playbooks to reflect the latest MITRE ATT&CK tactics, ensuring alignment with NIST’s incident response phases: preparation, detection, containment, eradication, and recovery. Conduct tabletop exercises simulating ransomware and supply chain attacks to validate escalation protocols. Post-drill reviews should address gaps, such as delayed stakeholder notifications or misconfigured backup retention policies.
Defensive reinforcements: mitigating exploit risks
Patch management and zero-day mitigation. Deploy critical security updates within 72 hours using automated tools like ManageEngine or WSUS. For legacy systems incompatible with patches, enforce compensatory controls: application whitelisting to block unauthorised binaries, network segmentation to isolate vulnerable OT/ICS systems, and memory protection via EDR solutions to detect exploit attempts.
Next-generation perimeter defences. Augment firewalls with intrusion prevention systems leveraging AI-driven anomaly detection. Threat prevention profiles automatically block traffic matching known attack patterns such as SQLi payloads and malicious PDFs. For cloud workloads, implement microsegmentation and east-west traffic monitoring to contain lateral movement.
Identity and access governance
Privileged access management. Adopt a Zero Trust model by restricting admin rights using Just-In-Time access frameworks. Privileged Access Workstations ensure administrative tasks occur on hardened devices with biometric authentication. Monitor for anomalous logins, such as off-hours access from unfamiliar geolocations, using UEBA platforms.
Credential hygiene and MFA enforcement. Replace static passwords with FIDO2 security keys or certificate-based authentication. For high-risk users (C-suite, sysadmins), implement phishing-resistant MFA systems. Automated scripts should disable inactive accounts and enforce password rotations aligned with NIST SP 800-63B guidelines.
Data integrity and recovery assurance
Immutable backups and cryptographic controls. Follow the 3-2-1 backup rule: three copies across two media types, with one stored offline. Encrypt backups using AES-256-GCM and manage keys via HSMs to prevent ransomware tampering. Test restoration weekly, simulating scenarios like database corruption, to validate recovery time objectives.
Countering social engineering and deepfakes
Phishing simulation and awareness training. Launch simulated campaigns to measure click-through rates. Train staff to identify QR code phishing and voice spoofing attacks. For C-level personnel, conduct personalised vishing drills mimicking executive impersonation.
Deepfake detection and OSINT monitoring. Integrate detectors to analyse media files for AI-generated artefacts, such as inconsistent eye blinking in videos. Deploy solutions to track brand impersonation campaigns on social platforms, flagging disinformation using NLP classifiers.
Supply chain risk mitigation
Third-party security posture assessments. Mandate SOC 2 Type II or ISO 27001 certifications for vendors accessing sensitive data. Conduct on-site audits to verify hardware and software bill of materials integrity. Contractually enforce breach notification timelines of six hours or less, per CERT-In directives.
Countering information warfare
Real-time disinformation takedowns. Collaborate with platforms to deplatform fake accounts amplifying false narratives. Deploy CERT-In’s fact-checking APIs to debunk rumours and issue counter-messaging via verified channels such as RSS feeds and official Telegram groups.
Critical infrastructure hardening
BFSI: implement quantum-resistant encryption for payment gateways and monitor ATM networks for jackpotting attacks.
Healthcare: isolate MRI and PACS systems on VLANs and deploy medical device firewalls.
Energy: use protocol whitelisting for SCADA systems and conduct red team exercises simulating grid shutdowns.
Regulatory coordination and public communications
Threat intelligence sharing. Subscribe to CISA’s Automated Indicator Sharing feed and contribute anonymised IoCs to sector-specific ISACs. Designate a liaison to coordinate with CERT-In during cross-border incidents.
Crisis communication frameworks. Pre-draft templated advisories for scenarios like data breaches, ensuring legal review for GDPR and HIPAA compliance. During outages, provide status updates via out-of-band channels such as SMS blasts and public radio.
Conclusion: building a culture of cyber vigilance
Cyber resilience transcends technology; it demands organisational alignment, from the boardroom to the help desk. By institutionalising war room protocols, enforcing least privilege, and fostering cross-sector collaboration, enterprises can transform from reactive defenders to proactive adversaries of cybercrime.
Disclaimer: this article provides generalised cybersecurity guidance. Consult legal and technical experts to tailor strategies to your organisation’s risk profile.
Instincts built hunting signals at sea, sharpened for two decades against digital adversaries. Not machine-written. Machine-proofread, comma by comma. Everything else, the noticing, the arguing, the getting it wrong sometimes, is mine. The bytes are for everyone; the opinions are only ever mine.
“Until the lion learns how to write, every story will glorify the hunter.” This is the lion's version.